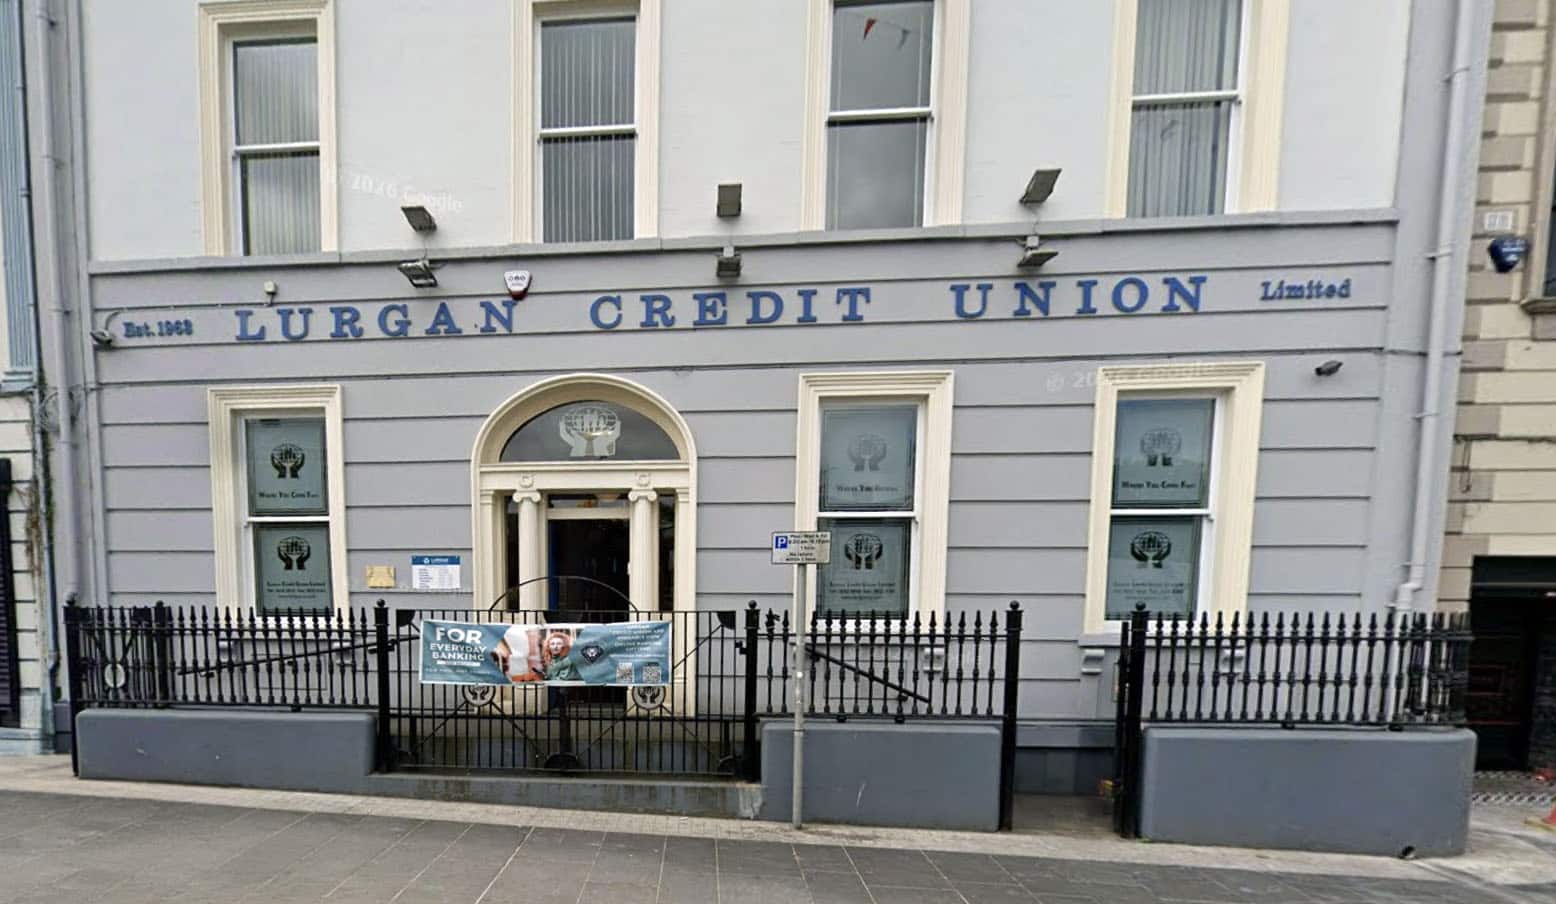
Lurgan Credit Union says an attacker exploited a vulnerability in its online banking platform, potentially accessing saved payee details — but members’ account balances and transaction information were not accessed.
The credit union said the incident affected an online platform operated by an external IT provider. A vulnerability was exploited between October 2 and 4 and closed on October 6, but the provider did not notify Lurgan Credit Union of the potential data exposure until November 16.
The provider’s investigation found that an unauthorised third party retrieved saved payee information linked to member accounts. It has not been possible to establish whether any, some or all of the saved information was taken. As a precaution, the provider is treating the details of all saved payees as potentially affected.
The information involved may include a payee’s bank account name and any nickname saved for them, their sort code and account number, and the payment reference entered by the member. The credit union said payment references are free text and may contain names, account references or other information. Internal reference numbers or codes were also among the affected data fields, but do not contain identifiable personal information.
Lurgan Credit Union said no phone numbers, home addresses or email addresses were included in the data. It added that member account details and balances, the number of transactions and the amounts involved were not accessed.
In a notice to members, the credit union said: “In general, given the limited nature of the personal data compromised for payees, we do not perceive that there is a risk of fraud, email or SMS phishing, identity theft or any other high-risk impact arising from this incident.”
It nevertheless advised members to remain alert to unexpected requests for personal or financial information, adding: “Lurgan Credit Union will never ask you for your online banking password or PIN.”
The credit union said it would continue reviewing information from its service provider and would contact identifiable individuals directly if further guidance or information was required under data protection law. It is also liaising with relevant authorities and said it would cooperate with their enquiries.